IFMs (AIFMs, ManCos) News

News and Example Templates for CSSF Circulars and EU Regulations for IFMs (AIFMs, ManCos)

Requirements of ICT Risk Management Framework Review Report

ICT Risk Management Framework Review Report Requirements in Luxembourg and EU under DORA

EU AI Act, NIS2, GDPR, PSD2, ISO, DORA Advisory, Templates, Trainings, Tools based in Luxembourg: ICT Risk Management Framework Review Report in Luxembourg and EU is a must to be submitted on a yearly basis for the financial and insurance

ICT Risk Management Framework Review Report Requirements in Luxembourg and EU under DORA Read More »
Operational guidance for incident handling under NIS2, HCPN, ANSSI, CSIRT, CIRCL, CSSF, ILR, GOVCERT.LU in Luxembourg - CSSF Press Release

Operational guidance for incident handling under NIS2, HCPN, ANSSI, CSIRT, CIRCL, CSSF, ILR, GOVCERT.LU in Luxembourg – CSSF Press Release

EU AI Act, NIS2, GDPR, PSD2, ISO, DORA Advisory, Templates, Trainings, Tools based in Luxembourg: Several major cybersecurity institutions in Luxembourg have collaborated to release a series of operational rulebooks designed to assist organizations in managing digital crises. These resources

Operational guidance for incident handling under NIS2, HCPN, ANSSI, CSIRT, CIRCL, CSSF, ILR, GOVCERT.LU in Luxembourg – CSSF Press Release Read More »

Multiple Critical Vulnerabilities in Citrix NetScaler ADC and NetScaler Gateway CVE-2026-88771, CVE-2026-88772, CVE-2026-88773, CVE-2026-88774, CVE-2026-88775, CVE-2026-88776, CVE-2026-88777, CVE-2026-88778 - CSSF Communication

Multiple Critical Vulnerabilities in Citrix NetScaler ADC and NetScaler GatewayCVE-2026-88771, CVE-2026-88772, CVE-2026-88773, CVE-2026-88774, CVE-2026-88775, CVE-2026-88776, CVE-2026-88777, CVE-2026-88778 – CSSF Communication

EU AI Act, NIS2, GDPR, PSD2, ISO, DORA Advisory, Templates, Trainings, Tools based in Luxembourg: The CSSF communication here and circl.lu report here detail several critical security vulnerabilities discovered in Citrix NetScaler ADC and Gateway products in 2026. Experts emphasize

Multiple Critical Vulnerabilities in Citrix NetScaler ADC and NetScaler GatewayCVE-2026-88771, CVE-2026-88772, CVE-2026-88773, CVE-2026-88774, CVE-2026-88775, CVE-2026-88776, CVE-2026-88777, CVE-2026-88778 – CSSF Communication Read More »

Active exploitation of a vulnerability on Cisco Secure Email Gateway - CSSF Communication

Active exploitation of a vulnerability, CVE-2026-76461, on Cisco Secure Email Gateway – CSSF Communication

Luxembourg Financial Regulatory Advisory, Tools, Templates: An active exploitation of a vulnerability, CVE-2026-76461, on Cisco Secure Email Gateway has been highlighted by CSSF Communication. Several international cybersecurity agencies have issued urgent warnings regarding a critical SQL injection vulnerability, identified as

Active exploitation of a vulnerability, CVE-2026-76461, on Cisco Secure Email Gateway – CSSF Communication Read More »

CSSF Annual Report 2025: Overview of the CSSF’s activities and initiatives in 2025 in Luxembourg

CSSF Annual Report 2025: Overview of the CSSF’s activities and initiatives in 2025 in Luxembourg

Luxembourg Financial Regulatory Advisory, Tools, Templates: In this article, we provide the excerpts from the CSSF Annual Report 2025, which outlines the activities and regulatory focus of Luxembourg’s financial supervisor. A central theme is the transformative impact of artificial intelligence, emphasizing its

CSSF Annual Report 2025: Overview of the CSSF’s activities and initiatives in 2025 in Luxembourg Read More »

Circular CSSF 26/915 on the applicability of the Digital Operational Resilience Act (DORA) to third-country branches in Luxembourg amending Circulars CSSF 20/750, 22/806, 25/881, 25/882, 25/883, 25/892 and 25/893

Circular CSSF 26/915 on the applicability of the Digital Operational Resilience Act (DORA) to third-country branches in Luxembourg amending Circulars CSSF 20/750, 22/806, 25/881, 25/882, 25/883, 25/892 and 25/893

Luxembourg Financial Regulatory Advisory, Tools, Templates: The Circular CSSF 26/915 establishes that the Digital Operational Resilience Act (DORA) officially applies to third-country branches (TCBs) operating within Luxembourg. This regulatory update follows a European Commission clarification confirming that these branches must meet the same ICT risk management and operational resilience standards

Circular CSSF 26/915 on the applicability of the Digital Operational Resilience Act (DORA) to third-country branches in Luxembourg amending Circulars CSSF 20/750, 22/806, 25/881, 25/882, 25/883, 25/892 and 25/893 Read More »

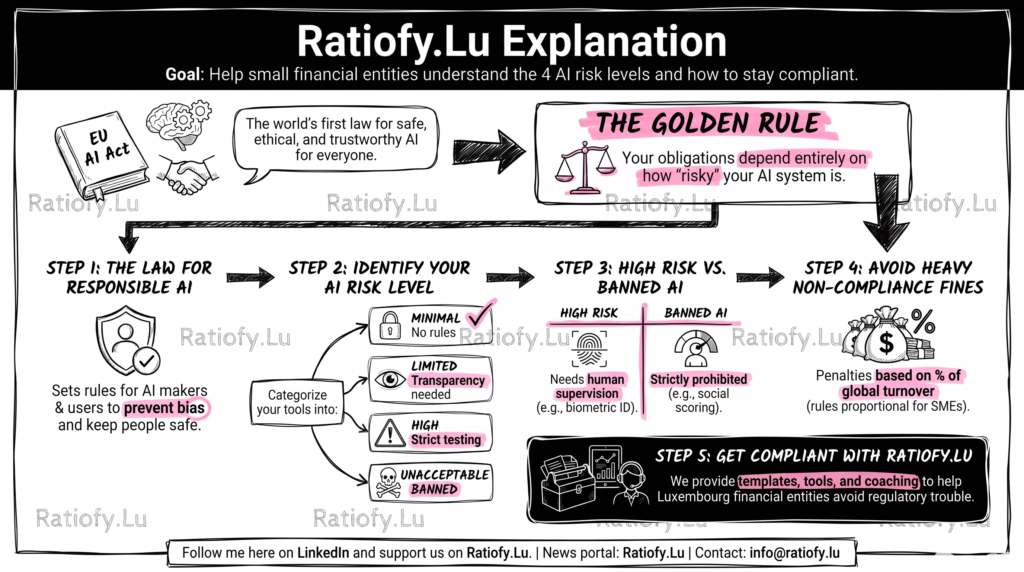
EU AI Act in Luxembourg and in EU, the world's first law on artificial intelligence, becomes mostly applicable now from August 2026

EU AI Act in Luxembourg and in EU, the world’s first law on artificial intelligence, becomes mostly applicable now from August 2026. Do you know what to do?

Luxembourg Financial Regulatory Advisory, Tools, Templates: The European Union’s AI Act in Luxembourg and in EU represents the first comprehensive legal framework designed to govern artificial intelligence by prioritizing safety, ethics, and transparency. As per the latest communication by European Council, most of the

EU AI Act in Luxembourg and in EU, the world’s first law on artificial intelligence, becomes mostly applicable now from August 2026. Do you know what to do? Read More »

CSSF Newsletter No 306 - July 2026 in Luxembourg-Ratiofy.Lu

CSSF Newsletter No 306 – July 2026 in Luxembourg. Do you know what it says?

Luxembourg Financial Regulatory Advisory, Tools, Templates: The CSSF Newsletter No 306 – July 2026 in Luxembourg serves as a comprehensive regulatory update for the Luxembourg financial sector as of July 2026. It highlights critical public warnings regarding fraudulent websites and identity theft while detailing new national regulations concerning

CSSF Newsletter No 306 – July 2026 in Luxembourg. Do you know what it says? Read More »

Warning of the European Systemic Risk Board (ESRB) of 25 June 2026 on systemic cyber risks stemming from frontier artificial intelligence models (FAIMs) (ESRB/2026/3). This can lead to serious problems…

Warning of the European Systemic Risk Board (ESRB) of 25 June 2026 on systemic cyber risks stemming from frontier artificial intelligence models (FAIMs) (ESRB/2026/3). This can lead to serious problems…

Luxembourg Financial Regulatory Advisory & Consulting: This official warning from the European Systemic Risk Board outlines the emerging cybersecurity threats posed by high-capacity Frontier AI Models to the financial sector. These advanced systems can autonomously identify software flaws and generate rapid attacks, potentially overwhelming the reactive patching

Warning of the European Systemic Risk Board (ESRB) of 25 June 2026 on systemic cyber risks stemming from frontier artificial intelligence models (FAIMs) (ESRB/2026/3). This can lead to serious problems… Read More »

Circular CSSF 26/914: Identification of obliged entities eligible for direct supervision by AMLA in Luxembourg. Ratiofy.Lu Explanation.

Circular CSSF 26/914: Identification of obliged entities eligible for direct supervision by AMLA in Luxembourg. Are you impacted?

Luxembourg Financial Regulatory Advisory, Tools, Templates: CSSF Circulars: The Circular CSSF 26/914 from the Commission de Surveillance du Secteur Financier (CSSF) outlines a mandatory data collection exercise for various Luxembourg-based financial institutions, including banks, investment firms, and crypto-asset providers. The primary objective is to

Circular CSSF 26/914: Identification of obliged entities eligible for direct supervision by AMLA in Luxembourg. Are you impacted? Read More »